


Convenience is not a luxury in exam preparation — it is how preparation survives a busy week. Prep4away offers multiple learning modes across multiple devices for the SC-300 Korean exam: 398 practice questions, printable, offline-capable, and tracked.
Microsoft SC-300 Korean Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Topic 1: Implement and manage identity monitoring and reporting | 25% | - Monitor identity environments
|
| Topic 2: Plan and implement identity governance | 25% | - Implement privileged access
|
| Topic 3: Implement authentication and access management | 25% | - Manage authorization
|
| Topic 4: Implement identity management | 25% | - Implement hybrid identity
|
SC-300 Korean Exam Questions and Answers
Prep4away issues a full refund if you take the Microsoft Identity and Access Administrator (SC-300 Korean Version) exam within 60 days of purchase and do not pass. The policy does not apply if the exam is taken within 3 days of purchase, if the exam was never actually taken, or to free materials or expired orders, and the candidate name must match the payer name. Submit a scan of your enrollment slip and the official Score Report PDF within 2 days of the exam; claims are processed within 7 days. Alternatively, exchange for two free exam products of equal value and keep your original update service. Orders arrive by email within 1 minute — contact support if nothing arrives within 2 hours.
The Microsoft Identity and Access Administrator (SC-300 Korean Version) exam contains 40-60 (approx.) to complete within 120 minutes. Knowing your pacing beforehand is exactly what the Prep4away Desktop Test Engine's timed simulations are for.
Online proctored or in-person at authorized Pearson VUE test centers Register for the Microsoft Identity and Access Administrator (SC-300 Korean Version) exam through these official channels:
After booking, Prep4away delivers your practice questions within 1 minute — preparation starts the same day.
Three versions of the same study materials, provided because different customers have various needs: a printable, expert-prepared PDF in Q&A form with free demo download and instant access; a Desktop Test Engine for Windows that simulates the real exam with two practice modes and works offline; and an Online Test Engine for any browser on Windows, Mac, Android, and iOS with test history and performance review. The 398 practice questions are identical across versions — just choose the one you like. All include 365 days of free updates, a 50% renewal discount afterward, and unlimited computer installations.
The official Microsoft Identity and Access Administrator (SC-300 Korean Version) outline defines 4 domains. The leading three are Implement and manage identity monitoring and reporting (25%), Implement authentication and access management (25%), and Plan and implement identity governance (25%). The full list is in the topics section above, and Prep4away's 398 practice questions cover each one.
No formal prerequisites required, but recommended knowledge of Microsoft Entra ID (Azure Active Directory), security fundamentals, and basic Azure administration. Since requirements change over time, confirm the latest on the official Microsoft exam page before scheduling.
The SC-300 Korean exam is a Microsoft certification exam validating the Microsoft Identity and Access Administrator (SC-300 Korean Version) syllabus shown above. It belongs to these credential paths: Microsoft Certified: Security, Compliance, and Identity Fundamentals, Microsoft Certified: Azure Administrator Associate, Microsoft Certified: Cybersecurity Architect Expert. Candidates in 2026 prepare for it with Prep4away's 398 practice questions, available as a printable PDF, a Windows Desktop Test Engine, and an Online Test Engine — three versions of the same materials.
The Microsoft Identity and Access Administrator (SC-300 Korean Version) exam requires 700 (out of 1000) to pass, and registration costs USD 165 (may vary by country/region). A failed attempt means paying the same fee again — a readiness check with the Prep4away engines before booking is the cheaper option.
Microsoft recommends these training resources for the Microsoft Identity and Access Administrator (SC-300 Korean Version) exam:
Follow the training with steady self-testing — the 398 practice questions from Prep4away make that routine easy to maintain.
Microsoft Identity and Access Administrator (SC-300 Korean Version) Sample Questions:
클라우드 기반 엔터프라이즈 앱이 포함된 Azure Active Directory(Azure AD) 테넌트가 있습니다.
내 앱 포털에서 관련 앱을 카테고리별로 그룹화해야 합니다.
무엇을 만들어야 할까요?
- A. 태그
- B. 컬렉션
- C. 명명 정책
- D. 동적 그룹
Correct Answer: B 🗳️
Explanation: Only visible for Prep4away members. You can sign-up / login (it's free).
귀하의 Microsoft 365 테넌트에는 다음 표에 표시된 관리 단위가 포함되어 있습니다.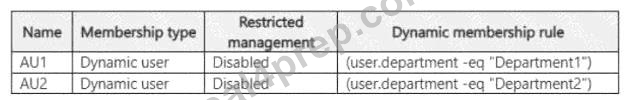
구독에는 다음 표에 표시된 관리자가 포함되어 있습니다.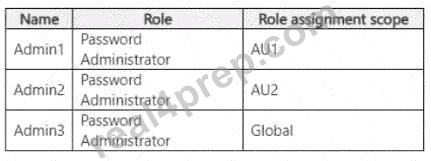
구독에는 다음 표에 표시된 사용자가 포함됩니다.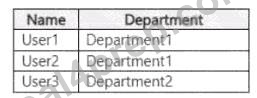
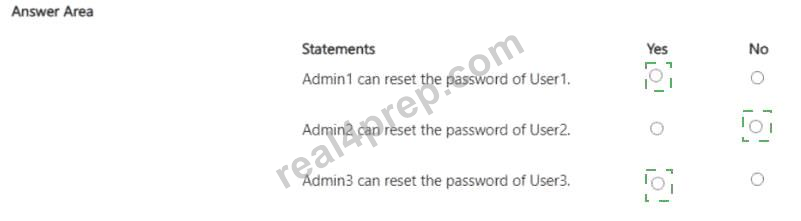
다음 각 문장에 대해, 문장이 사실이면 '예'를 선택하고, 그렇지 않으면 '아니요'를 선택하십시오.
참고: 정답 하나당 1점입니다.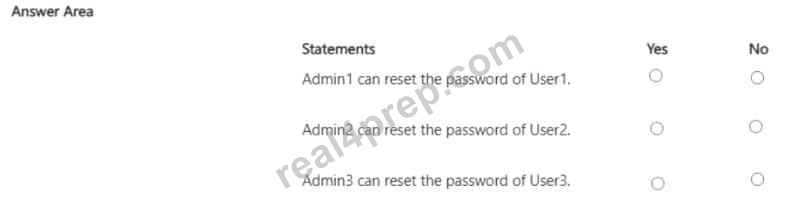
Correct Answer:
Explanation: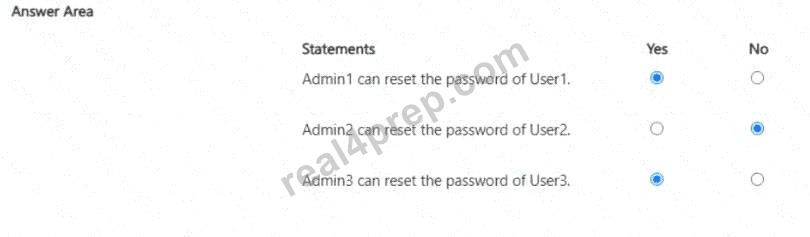
In Microsoft Entra ID, Administrative Units (AUs) are logical groupings that allow delegation of administrative permissions over specific subsets of users or groups. This delegation follows scope-based role assignment principles. The Password Administrator role enables resetting user passwords, but only within the assigned scope (either at the AU level or globally).
Let's analyze the scenario step by step:
Administrative Units and Membership Rules
AU1 includes users where (user.department -eq " Department1 " ) # so User1 and User2 belong to AU1.
AU2 includes users where (user.department -eq " Department2 " ) # so User3 belongs to AU2.
Role Assignments
Admin1: Password Administrator for AU1 # can manage password operations for User1 and User2.
Admin2: Password Administrator for AU2 # can manage password operations for User3.
Admin3: Password Administrator at Global scope # can reset passwords for all users in the tenant.
Access Evaluation
Admin1 # User1: Yes, because User1 is in AU1.
Admin2 # User2: No, because Admin2's scope (AU2) doesn't include User2, who is in AU1.
Admin3 # User3: Yes, because Admin3 has global scope and can manage all users.
However, note that Admin2 can only reset User3's password because User3 belongs to AU2.
Thus, applying SC-300 documentation logic:
"Administrators can perform their role's permitted actions only on objects within their administrative unit scope, unless their role assignment is global."
귀하는 다음 표에 표시된 사용자가 포함된 Microsoft Entra 테넌트를 보유하고 있습니다.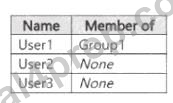
App1이라는 이름의 엔터프라이즈 애플리케이션을 추가하고 다음과 같은 셀프 서비스 설정을 구성합니다.
* 사용자가 이 애플리케이션에 대한 액세스 권한을 요청할 수 있도록 허용하시겠습니까? 예
* 할당된 사용자를 어느 그룹에 추가해야 합니까?: 그룹1
* 이 애플리케이션에 대한 접근 권한을 부여하기 전에 승인이 필요합니까?: 예
* 이 애플리케이션에 대한 접근 권한을 승인할 수 있는 사람은 누구입니까? 사용자2
어떤 사용자가 앱1에 대한 접근 권한을 요청할 수 있나요?
- A. User2 및 User3만 해당
- B. User1과 User3만 해당
- C. User3만 해당
- D. 사용자1, 사용자2, 그리고 사용자3
Correct Answer: B 🗳️
귀하의 Azure 구독에는 다음 표에 표시된 키 자격 증명 모음이 포함되어 있습니다.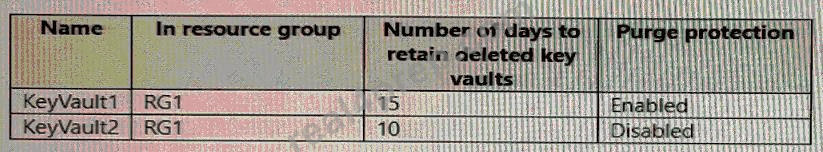
구독에는 다음 표에 표시된 사용자가 포함됩니다.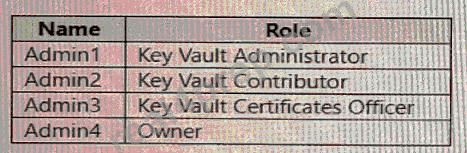
6월 1일, Admin4는 다음과 같은 작업을 수행합니다.
* Key Vault1에서 Certificate!라는 이름의 인증서를 삭제합니다.
* KeyVault2에서 Secret1이라는 이름의 비밀 키를 삭제합니다.
다음 각 문장에 대해, 문장이 사실이면 '예'를 선택하고, 그렇지 않으면 '아니요'를 선택하십시오.
참고: 정답 하나당 1점입니다.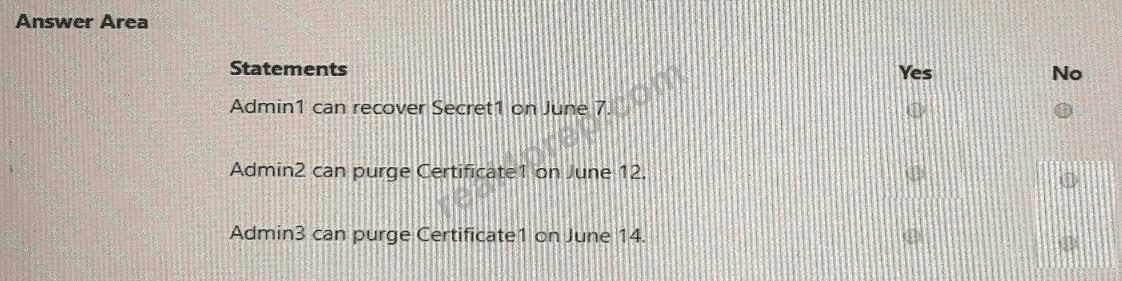
Correct Answer:
Explanation: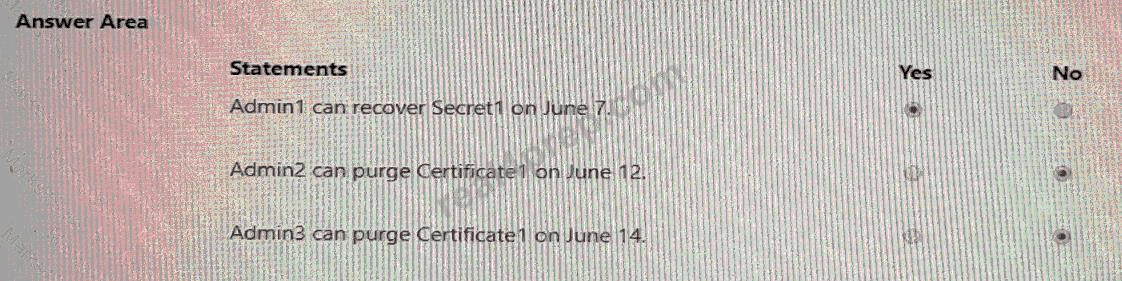
Azure Key Vault uses soft delete with a configurable retention period (7-90 days). During this window, deleted objects can be recovered, and if purge protection is enabled, they cannot be purged until the retention period expires. The SC-300 materials describe: "Soft-delete retains keys, secrets, and certificates for the configured retention days. When purge protection is enabled, even users with purge permission cannot permanently delete objects before the retention period ends; objects remain recoverable until expiry." The Key Vault RBAC data-plane roles further clarify capabilities. The guide states: "Key Vault Administrator has full data actions, including recover and purge across keys, secrets, and certificates. Key Vault Contributor manages the vault resource and settings but does not have data-plane permissions to read, delete, purge, or recover objects. Certificates Officer can manage and recover certificates but is not granted purge." Applying this:
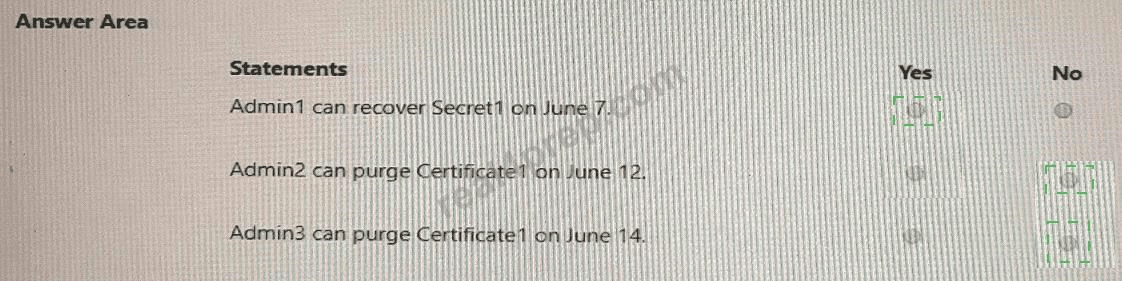
Secret1 was deleted on June 1 from KeyVault2 (retention 10 days, purge protection Disabled). If it hasn't been purged, it is recoverable any time through June 11. Admin1 (Key Vault Administrator) therefore can recover on June 7.
Certificate1 was deleted on June 1 from KeyVault1 (retention 15 days, purge protection Enabled). Purge is blocked until June 16 regardless of role. Additionally, Admin2 (Key Vault Contributor) lacks data-plane purge rights. Hence cannot purge on June 12.
Admin3 (Key Vault Certificates Officer) also lacks purge permission; with purge protection still in effect, cannot purge on June 14.
Microsoft 365 테넌트가 있습니다.
모든 사용자는 Microsoft 365 서비스에 액세스할 때 다단계 인증(MFA)을 위해 Microsoft Authenticator 앱을 사용해야 합니다.
일부 사용자는 로그인 요청을 시작하지 않았는데도 Microsoft Authenticator 앱에서 MFA(다단계 인증) 메시지가 표시되었다고 보고했습니다.
사용자가 본인이 시작하지 않은 MFA 요청을 신고할 경우 자동으로 해당 사용자를 차단해야 합니다.
해결 방법: Azure 포털에서 다단계 인증(MFA)에 대한 사용자 차단/차단 해제 설정을 구성합니다.
이것이 목표를 달성합니까?
- A. 아니요
- B. 네
Correct Answer: B 🗳️
Explanation: Only visible for Prep4away members. You can sign-up / login (it's free).
Viewing page 1 out of 80 pages.
Viewing questions 1-5 out of 398 questions.


